Fintech developers require more than just endpoint references; they need a reliable roadmap to navigate complex regulatory and financial workflows. Implementing robust best practices for API documentation in fintech is the most effective way to reduce integration friction, ensure regulatory compliance, and accelerate developer onboarding.
By moving beyond simple endpoint lists to provide context-aware, secure, and actionable technical guides, fintech companies can significantly lower support overhead and improve the overall developer experience. When crafting these guides, it is helpful to remember blockchain content marketing best practices to ensure your technical communication remains accessible and clear.
Limitations of schema-first generation
Tools like Swagger or Redoc are excellent for visualizing endpoint parameters, but they are inherently static and context-blind. They fail to communicate the regulatory constraints, idempotency requirements, or the specific sequence of operations required to maintain ledger integrity.
Relying solely on auto-generated specs leaves developers guessing about the lifecycle of a payment. This often leads to integration errors that only manifest during production reconciliation.
Essential best practices for API documentation in fintech
To reduce integration friction, documentation must prioritize the developer’s mental model of the financial workflow. The following best practices for API documentation in fintech emphasize clarity, safety, and operational transparency:
- Use custom error objects: Move beyond standard HTTP codes to provide actionable feedback like
INSUFFICIENT_FUNDSorKYC_PENDING. - Maintain sandbox parity: Ensure the test environment mirrors production, including simulated network timeouts and partial failures.
- Implement clear versioning: Use URI or header-based versioning with explicit deprecation policies to protect long-term stability.
- Mask sensitive data: Never use real PII or PCI-DSS data in public examples; use clear, masked placeholders instead.
- Provide sequence diagrams: Use visual flows to explain complex multi-step processes like OAuth handshakes or ledger reconciliation.
Contextualizing error codes for financial transactions
Standard HTTP status codes like 400 or 500 are insufficient for complex financial systems. Fintech APIs should implement custom error objects that provide actionable feedback.
Including a unique request trace ID in every error response allows developers to correlate issues with internal logs, significantly accelerating the debugging process. This level of detail transforms a generic error into a self-service troubleshooting opportunity.
Sandbox environment parity
Documentation is useless if the sandbox environment behaves differently than production. Developers need a mirror image of the production environment, including support for edge cases like simulated network timeouts, partial transaction failures, and webhook delivery retries.
If the documentation describes a feature that the sandbox cannot replicate, the trust in the entire API platform erodes. Providing a Binance API Guide: Automate Your Crypto Trading is a highly effective way to guide developers through complex scenarios.
Fallacy of the static documentation portal
Fintech APIs are living products, yet many companies treat documentation as a static artifact. A static PDF or a stale wiki page is a liability that guarantees developer frustration and increased support overhead.
Instead, treat your documentation as code, allowing for continuous updates alongside feature releases.
Versioning strategies for regulatory compliance
Financial integrations often require long-term stability. Implementing a clear versioning strategy—such as URI versioning (/v1/) or header-based versioning—is essential.
Documentation must explicitly state the deprecation policy and provide migration guides for every breaking change, ensuring that compliance-heavy clients can upgrade their systems without service disruption. Always maintain a “Changelog” that highlights security patches separately from feature updates.
Security disclosure versus documentation clarity
Transparency is vital, but exposing internal system architecture in documentation can create security vulnerabilities. The goal is to provide enough information for a developer to integrate successfully without revealing the underlying infrastructure or internal security controls.
As the middle east fintech landscape continues to evolve, maintaining this balance between transparency and security becomes a critical competitive advantage.
Handling sensitive data fields in public specifications
Public documentation should never contain real PII or PCI-DSS sensitive data. Use clear, masked examples in your request/response bodies.
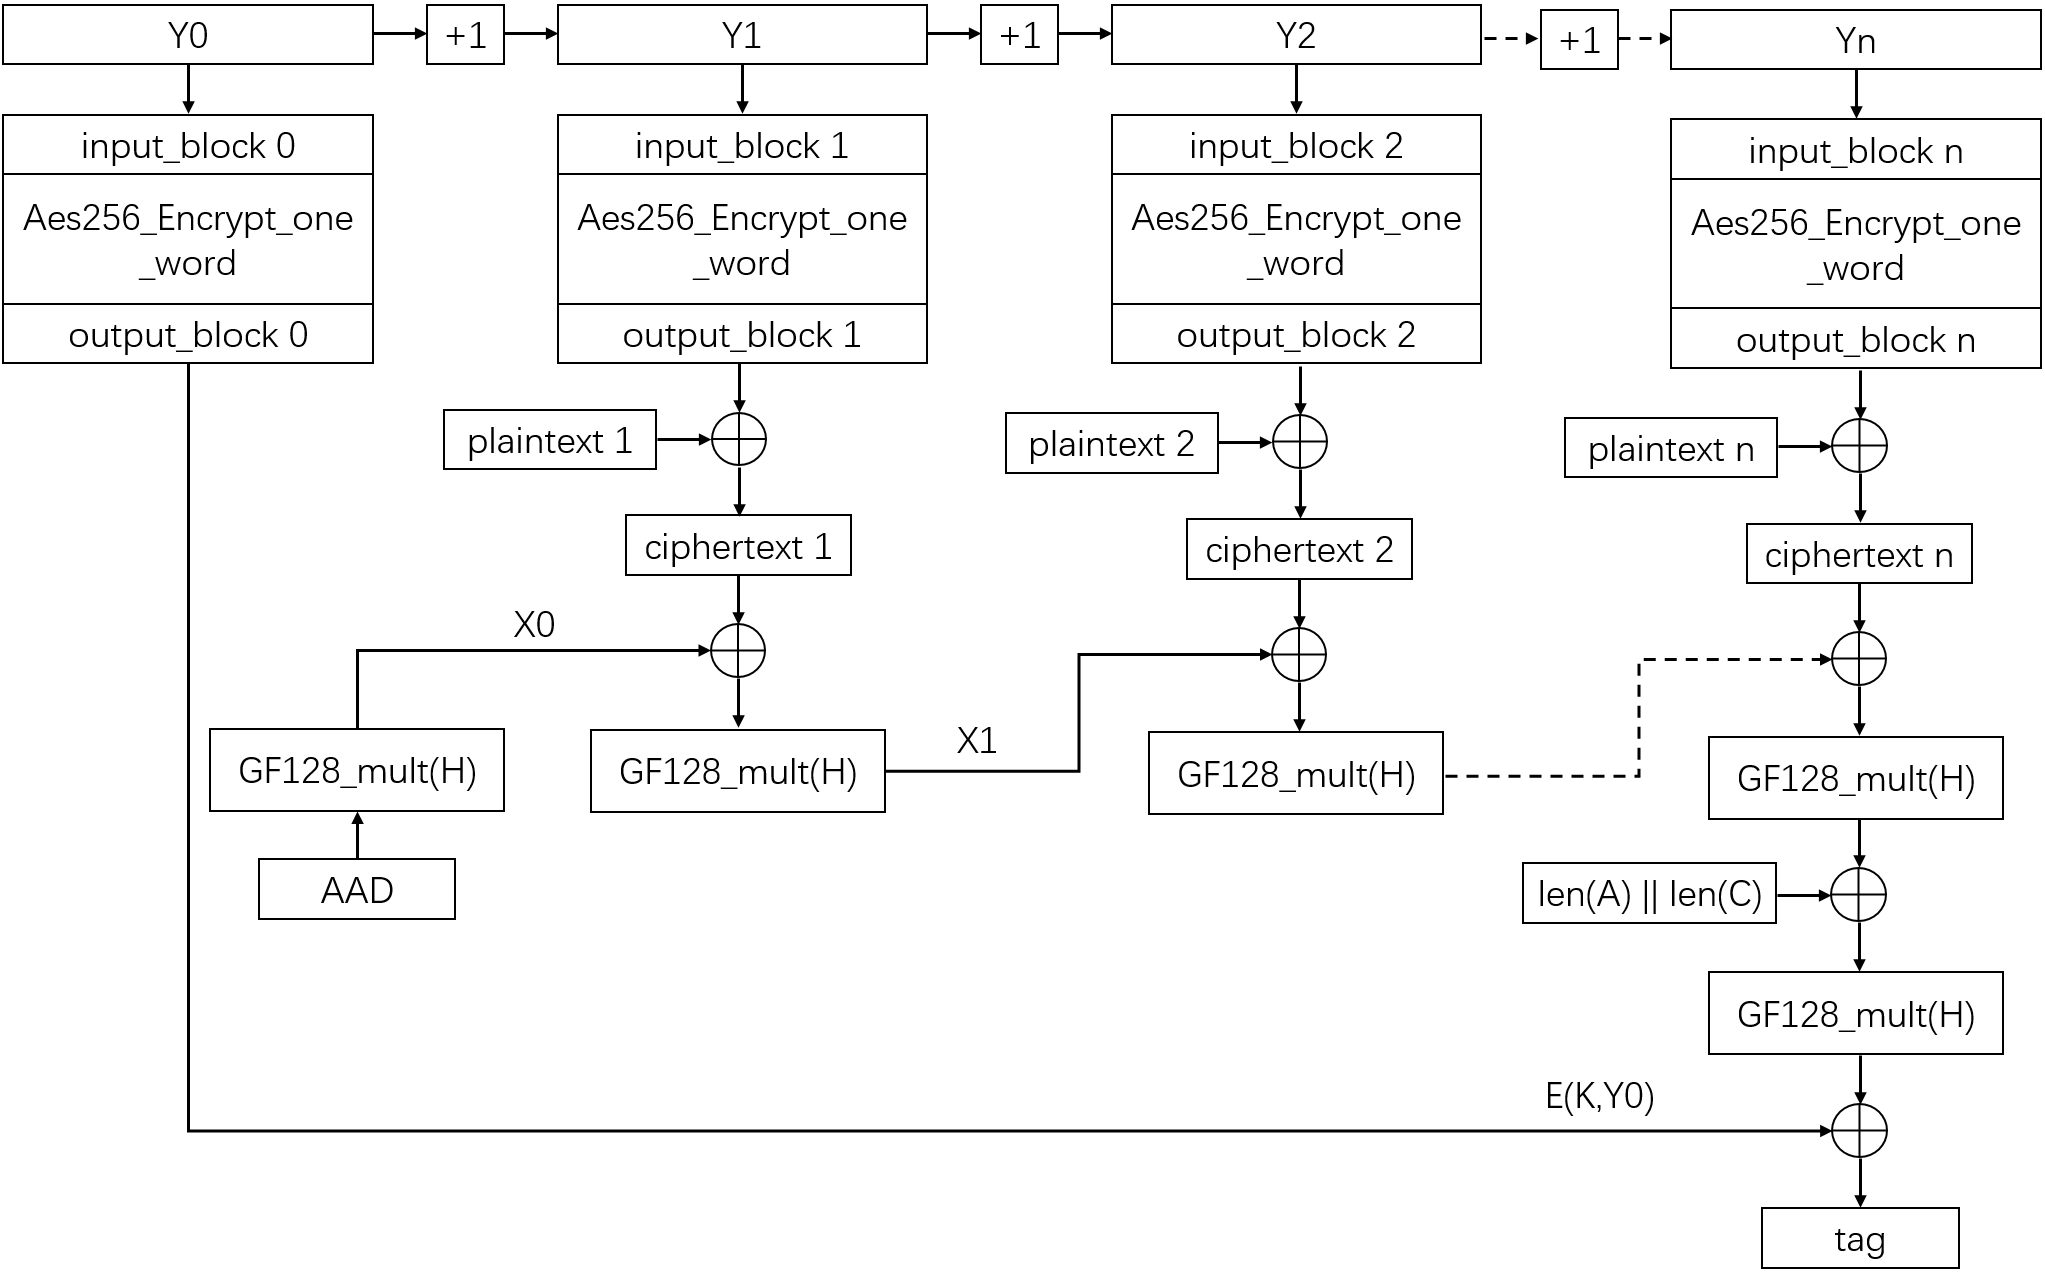
When documenting fields that require encryption, provide specific guidance on the required algorithms (e.g., AES-256-GCM) and key management practices, rather than just listing the field as a string. This ensures developers implement security correctly from the first line of code.
Developer experience metrics that actually matter
Volume of documentation is a vanity metric; the only number that matters is the time it takes for a developer to make their first successful API call. This metric reflects the quality of your onboarding flow and the clarity of your technical writing.
By tracking “Time to First Hello World” (TTFHW), teams can identify exactly where developers drop off in the integration funnel.
Measuring integration success
Analyze support ticket data to identify recurring themes in integration failures. If developers consistently struggle with a specific authentication flow or webhook signature verification, it is a clear signal that the documentation for that section is insufficient.
Use this data to iteratively improve your guides, turning common support hurdles into self-service solutions. Regularly auditing your documentation against these support tickets ensures that your content evolves alongside the actual challenges your users face.
Frequently Asked Questions
Definition of digital wallet interoperability
Digital wallet interoperability is the ability for different payment systems and wallets to exchange funds and data seamlessly, allowing users to transact across diverse platforms.
Importance of interoperability standards for fintech
These standards prevent market fragmentation, reduce transaction costs, and foster competition by allowing smaller fintech players to integrate with larger financial ecosystems.
Impact of ISO 20022 standards on digital wallets
ISO 20022 provides a common language for financial messaging, enabling wallets to process richer data sets, which improves transparency and automated reconciliation in cross-border payments.
Global standards for mobile wallet payments
While there is no single global standard, organizations like EMVCo and the ISO provide frameworks that many mobile wallet providers adopt to ensure security and compatibility.
Primary risks of cross-platform wallet integration
The primary risks include security vulnerabilities during data transmission, inconsistent compliance with anti-money laundering (AML) protocols, and potential data privacy leaks.
- Real-world performance of digital wallet interoperability standards in open-loop systems
- Market expansion pathways leveraging the benefits of cross-border digital wallet interoperability
- Technical frameworks on how to achieve interoperability between mobile wallets
- Reality check on security risks in cross-platform wallet transactions